About me
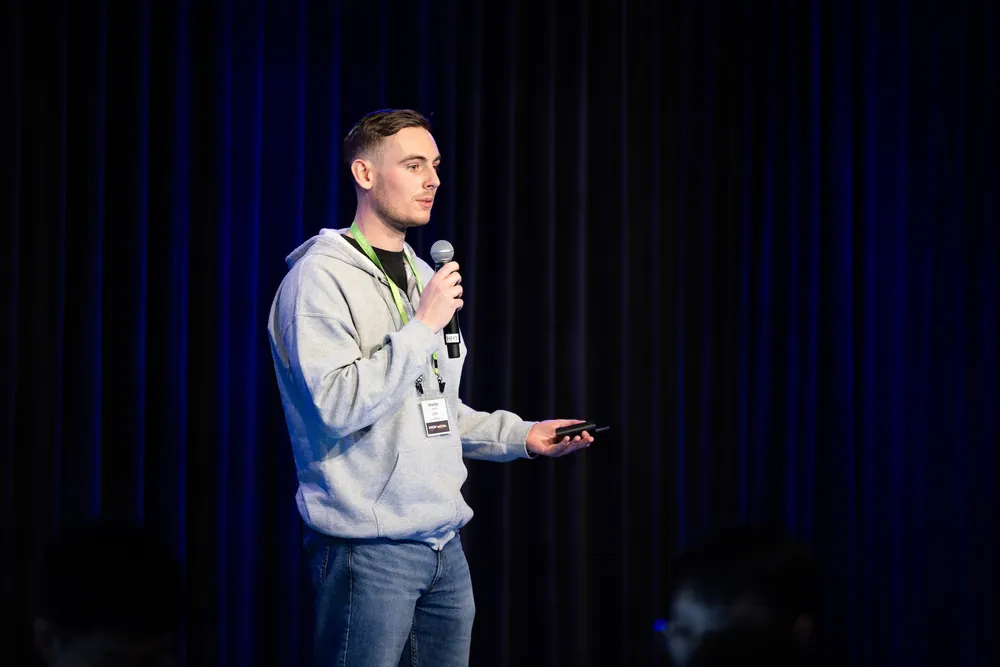
Hey, I’m Brandyn.
I’m a full-time bug bounty hunter, founder of MurtaSec, co-host of Critical Thinking Bug Bounty Podcast, and public speaker.
The Journey
My journey in cybersecurity started at 16 in sysadmin and blue team roles, before moving into pentesting and eventually appsec. In my younger years, I was addicted to building home labs, pwning every lab I could find, and collecting certifications along the way: CompTIA A+, Net+, Sec+, CCNA, OSCP, CRT, OSWE, and the list goes on.
12 years later, I’ve been fortunate to work alongside some of the most talented security teams, researchers, and bug bounty hunters in the industry. Along the way, I’ve built rich consulting experience and an incredible network of founders, CISOs, pentesters, blue teamers, appsec engineers, and clients, many of whom have become friends.
Two years ago, I made the leap into bug bounty. Within a year, I went full-time. Haven’t looked back.
In that time, I’ve won awards at live hacking events for most critical bug, most criticals (both individually and as a team), most creative bug, and best written report, several of them on AI-focused programs including Amazon’s Nova and Alexa models.
It’s also led to me being featured as an industry expert by The Wall Street Journal, the BBC, ITV, Good Morning Britain, GB News, The Sun and Cybercrime Magazine.
Why This Site
I built this site because I’ve always wanted a platform to write about security research, bugs I’ve found, and the people I’ve worked with.
Bug bounty gave me the freedom to explore and spend time on research, side projects, security and local AI. I figured it was time I started writing about some of it.
What I Do Now
Bug Bounty Hunting
Full-time hunter on HackerOne and Bugcrowd. Specializing in web applications, APIs, and AI/LLM security.
Critical Thinking Podcast
Co-host alongside Rhynorater and rez0. We discuss bug bounty methodology, new vulnerabilities, and the business of hacking.
MurtaSec
My penetration testing company specialising in Web, API, and AI red team assessments. Built by some of the best hunters, security researchers and testers, doing some seriously cool work.
Get in Touch
I’m available for consulting, strategy, advisory, and speaking engagements.
Want me to speak, consult, or red-team?
Available for speaking engagements, consulting, strategy, advisory, and penetration testing through MurtaSec.